Published on 22/3/2026; reflects the information and wording at that time. For AIST's current position see Setting the record straight and the Parents' Common Voice.

Immediately upon identifying potential "loopholes" in data access control:
- The Supervisory Board conducted a review, assessed risks, and took emergency action
- A binding mechanism was immediately proposed to the Legal Board for development (February 27, 2026).
👉 AIST's Principle:
We do not wait for issues to arise before taking action
We proactively prevent them
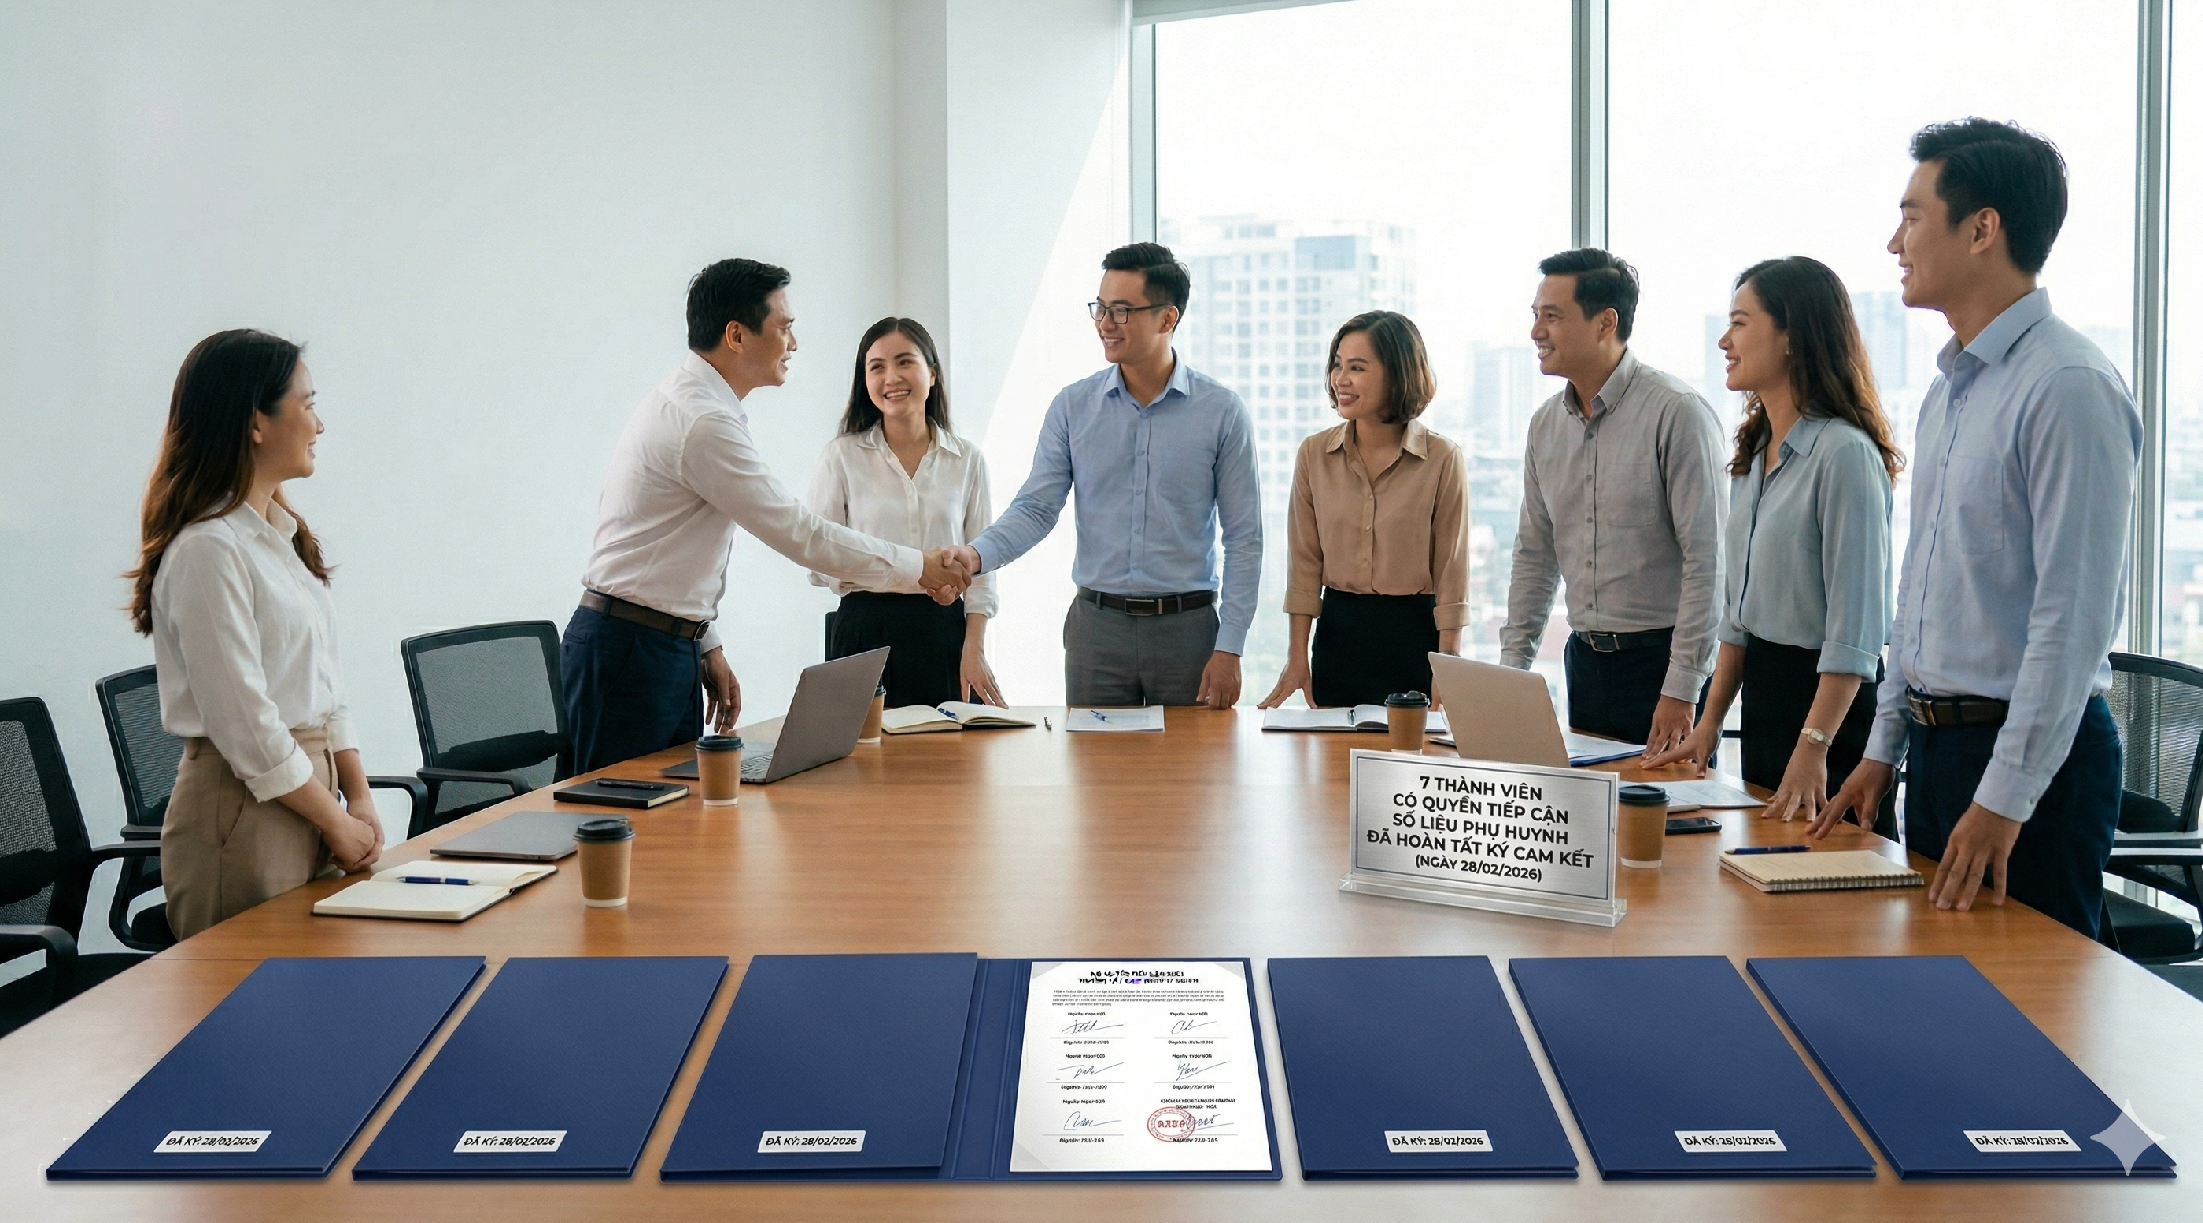
Image for illustrative purposes only
- February 27: Announced and requested legal templates from lawyers; re-drafted to fit requirements and submitted to the Legal Board for final review and editing before printing.
- February 28: Officially approved and signed in person during the Extraordinary General Meeting (EGM)
👉 All individuals with data access rights (07/10 members):
- Signed a Confidentiality Commitment
- Certified with the AIST official seal
- Applied equally – no exceptions – regardless of role
(Below is an image of the signed document, showing one representative copy)

The commitment clearly stipulates:
- Access data only within the scope of assigned tasks
- Strictly no usage for personal gain
- No marketing, no exploitation, and no external sharing
- No unauthorized copying or distribution of data
This is more than just an internal policy 👉 It is a legally binding obligation
Parents can rest assured—and are invited to proactively monitor this alongside AIST
AIST Commits:
👉 Parent personal data must be protected with the highest level of seriousness
Additionally, parents are encouraged to:
- Proactively report any signs of irregularity
- Email AIST’s official address below for immediate action if you notice any signs of disturbance or if your information is being misused for personal purposes...
AIST Commits: Protecting parents' personal data with actions, not just words.